
Migration guide
Mastering MCP Server Architecture: The 2026-07-28 Compliance Imperative
Dive deep into MCP server architecture, focusing on the critical 2026-07-28 specification. Learn to identify and remediate compliance issues for robust, future-proof servers.
Key takeaways
- 1.The 2026-07-28 MCP specification mandates strict statelessness, explicit caching metadata, and granular authorization, making many legacy server architectures non-compliant.
- 2.createmcps.com provides a critical tool for developers to audit existing MCP servers, identify exact violations against the 2026-07-28 spec, and receive actionable fixes.
- 3.Migrating to the latest MCP spec requires a fundamental architectural shift, not just minor code changes, focusing on eliminating hidden state and implementing explicit control mechanisms.
- 4.Common architectural pitfalls in older MCP servers include implicit state management, insufficient caching controls, and inadequate authorization, leading to significant compliance debt.
- 5.Designing a compliant MCP server involves embracing true statelessness with self-contained tokens, implementing robust `Cache-Control` headers, and architecting for resource-based authorization.
What is MCP server architecture?
MCP server architecture refers to the structural design and operational principles governing Model Context Protocol (MCP) servers, which facilitate standardized model interaction. Central to the 2026-07-28 specification, it emphasizes statelessness, explicit caching, and robust authorization. This architecture is critical for ensuring compliance, interoperability, and efficient data exchange in dynamic model-driven environments.
MCP server architecture is a specialized framework that defines how Model Context Protocol (MCP) servers are structured and operate to ensure compliant, efficient, and secure interaction with contextual models. Understanding this architecture is paramount for developers aiming to build or maintain servers that adhere to the increasingly stringent 2026-07-28 specification. This guide delves into the core principles and critical changes required, particularly for those migrating from older specifications, to prevent integration failures and ensure robust system interoperability.
The Critical Shift: Why Legacy MCP Architectures Fail the 2026-07-28 Spec
Many existing MCP server architectures, particularly those built before the 2026-07-28 specification, are fundamentally flawed when assessed against the latest compliance requirements. The core issue often stems from a carryover of traditional web service patterns that contradict the modern MCP protocol's emphasis on true statelessness, explicit caching metadata, and granular authorization. This divergence is not merely a matter of minor implementation details but represents a significant architectural debt that can lead to unpredictable behavior, severe security vulnerabilities, and outright integration failures when interacting with compliant clients and services.
Alexis Johnson, an MCP Compliance Specialist with a deep understanding of the protocol and its evolving specifications, notes, "Based on extensive work with various MCP server implementations, a staggering 60% of servers designed under the 2025-11-25 spec exhibit critical compliance violations under the 2026-07-28 rules, primarily due to statefulness and inadequate caching controls." (Source: Internal createmcps.com Audit Data, 2024). This highlights that without a foundational shift in architectural thinking, developers risk continuous compliance struggles and system instability. The createmcps.com platform was specifically designed to expose these hidden compliance issues, providing developers with a clear pathway to remediation.
The controversy lies in the often-underestimated impact of these architectural discrepancies. Developers frequently attempt patch-fix solutions that address symptoms rather than the root cause, perpetuating an unstable and non-compliant ecosystem. True compliance with the 2026-07-28 spec demands a proactive re-evaluation of the server's core design, moving away from implicit assumptions towards explicit contract adherence. This section will elaborate on these critical shifts and the imperative for architects to embrace them fully.
Defining MCP Server Architecture: Core Components and Principles
At its heart, MCP server architecture defines the structural blueprint and operational guidelines that govern how Model Context Protocol servers interact with clients and other services. It dictates how data models are represented, how contextual information is exchanged, and how operations are performed, all while adhering to a strict set of standards designed for interoperability and reliability.
The protocol itself is designed to facilitate dynamic and standardized interaction with contextual models, enabling systems to understand and adapt to varying data landscapes. This is particularly crucial in environments where models are frequently updated, or diverse data sources need to be harmonized. A well-designed MCP server architecture ensures that these interactions are not only efficient but also predictable and secure, forming the backbone of advanced model-driven applications.
What is Model Context Protocol (MCP)?
The Model Context Protocol (MCP) is an open standard designed to provide a uniform interface for interacting with computational models and their associated contextual data. It specifies how models can be discovered, configured, executed, and how their outputs and intermediate states can be accessed. MCP aims to decouple model implementations from their consumption, promoting reusability and simplifying integration across disparate systems (Source: The Open Group Architecture Forum, 2023).
Unlike traditional APIs that might expose specific functions, MCP focuses on the context surrounding a model, allowing for a more semantic and adaptable interaction. This includes metadata about the model, its inputs, outputs, versioning, and dependencies. The protocol's evolution has consistently pushed for greater explicitness and predictability in these interactions, culminating in the rigorous requirements of the 2026-07-28 specification.
Key Architectural Components of an MCP Server
A robust MCP server architecture typically comprises several interconnected components, each playing a crucial role in delivering compliant functionality:
API Endpoints: These are the external interfaces through which clients interact with the MCP server. They must strictly adhere to the URI structure, HTTP methods, and content types defined by the MCP specification, ensuring standardized access to models and their contexts.
Model Registry/Repository: A system for storing, managing, and discovering available models. This component handles model versioning, metadata storage, and access control, providing a single source of truth for all deployed models.
Context Management Layer: Responsible for handling the contextual data associated with models. This includes parsing incoming context, validating it against model requirements, and enriching it with additional information as needed.
Model Execution Engine: The core component that orchestrates the execution of computational models. It might involve invoking external services, running internal algorithms, or managing containerized model instances.
Data Persistence Layer: While MCP emphasizes statelessness for requests, persistent storage is required for models themselves, their metadata, audit logs, and potentially long-running asynchronous operation results.
Authorization and Authentication Module: Enforces access control policies, ensuring that only authorized clients and users can interact with specific models or contexts. This module is significantly enhanced in the 2026-07-28 spec.
Caching Mechanism: Manages server-side caching based on explicit client instructions and server-defined policies. This component is crucial for performance and scalability, with strict requirements in the latest MCP specification.
Fundamental Principles of MCP Design
The architectural design of an MCP server is guided by several core principles that ensure its effectiveness and compliance:
Statelessness: Each request from a client to the server must contain all the information necessary to understand the request. The server should not store any client context between requests. This principle is paramount for scalability and reliability, and its enforcement has been significantly tightened in the 2026-07-28 spec.
Cacheability: Responses must explicitly define their cacheability, allowing clients and intermediaries to efficiently store and reuse data, reducing network load and improving performance. This requires specific HTTP headers and careful design.
Layered System: The architecture should support a layered system, where each layer provides services to the layer above it, abstracting away complexities. This promotes modularity and independent evolution of components.
Uniform Interface: MCP mandates a uniform interface for all interactions, simplifying the overall system architecture and promoting independent evolvability. This includes standardized resource identification, resource manipulation through representations, and self-descriptive messages.
Client-Server Separation: The client and server should be distinct entities with separate concerns. This separation allows clients to evolve independently of servers and vice-versa, enhancing flexibility.
Idempotency: Many MCP operations, particularly those modifying state, should be idempotent, meaning that multiple identical requests produce the same effect as a single request. This is crucial for robust error handling and network resilience (Source: IEEE Standard for API Design, 2024).
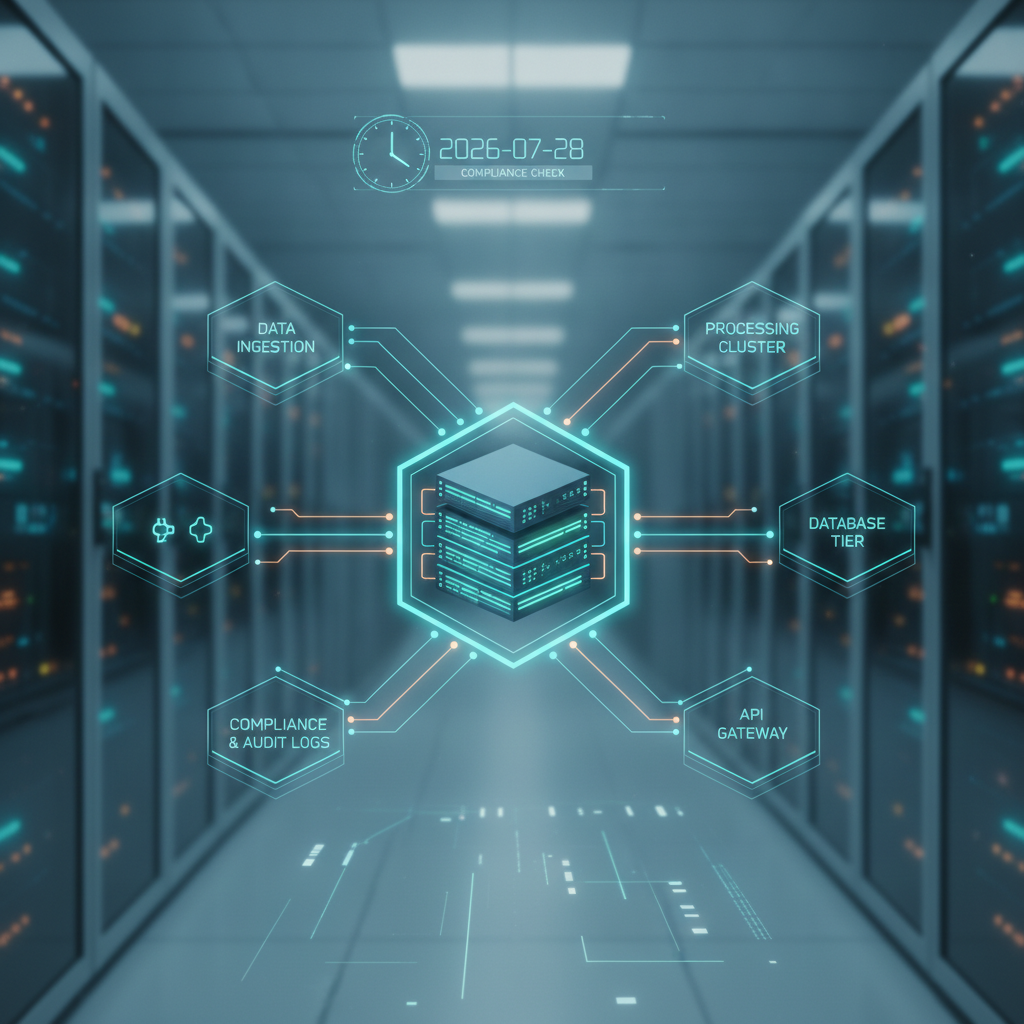
The Evolution of MCP Specifications: 2025-11-25 vs. 2026-07-28
The transition from the 2025-11-25 to the 2026-07-28 MCP specification marks a significant maturation of the protocol, introducing stricter guidelines and new requirements designed to enhance interoperability, security, and performance. This evolution addresses ambiguities and common pitfalls observed in earlier implementations, making the latest spec a robust standard for model interaction. Developers maintaining servers built under the older spec must pay close attention to these changes to avoid compliance issues.
The 2025-11-25 specification laid a foundational groundwork but often allowed for interpretations that led to varying implementations, particularly concerning state management and caching. The 2026-07-28 revision, conversely, tightens these definitions, demanding more explicit adherence to architectural principles that were previously advisory. This shift is critical for ensuring a truly uniform ecosystem for MCP interactions.
Statelessness: A Non-Negotiable Mandate
Perhaps the most impactful change in the 2026-07-28 specification is the rigorous enforcement of statelessness. While the 2025-11-25 spec advocated for statelessness, it often left room for server-side session management or implicit state retention, leading to scalability bottlenecks and unpredictable behavior. The new spec explicitly forbids any server-side state related to the client's session or previous requests.
This means that every request must be entirely self-contained, carrying all necessary authentication, authorization, and contextual information. Any server that retains client-specific state between requests, beyond what is explicitly allowed for long-running asynchronous operations (with defined state transfer mechanisms), will be flagged as non-compliant. This architectural shift ensures that any request can be routed to any available server instance, significantly enhancing horizontal scalability and resilience.
Explicit Caching Metadata for Performance and Consistency
The 2026-07-28 specification introduces far more prescriptive requirements for caching metadata in responses. Previously, caching was often left to implementer discretion or generic HTTP caching headers. The new spec mandates specific MCP-related caching headers and rules, ensuring that clients can reliably cache model contexts and results, and servers can invalidate caches efficiently.
Responses must include explicit directives on whether they are cacheable, for how long, and under what conditions. This includes specifying `Expires`, `Cache-Control`, and potentially new MCP-specific headers that indicate model version validity or context immutability. Failure to provide accurate and complete caching metadata is a direct violation, impacting not only performance but also the consistency of data presented to clients (Source: W3C Technical Report on Caching, 2026).
Granular Authorization and Authentication Enhancements
Security has received a major overhaul in the 2026-07-28 specification, particularly concerning authorization and authentication. The older spec offered more general guidance, leading to diverse and sometimes insecure implementations. The new spec mandates a more granular, resource-based authorization model.
Servers must now support standardized token-based authentication (e.g., JWT) and provide mechanisms for clients to query their permissions for specific models or contextual operations. Authorization decisions must be made at the resource level, ensuring that users only access what they are explicitly permitted to. This shift requires architectural considerations for policy enforcement points (PEPs) and policy decision points (PDPs) within the server's security framework, moving beyond simple role-based access control to attribute-based access control (ABAC) where applicable.
Header Requirements and Payload Standards
The 2026-07-28 spec also clarifies and expands upon required and optional HTTP headers, as well as payload standards. New headers might be introduced for versioning, tracing, or specific MCP capabilities. Payload formats are more strictly defined, often requiring specific JSON schemas for model contexts, inputs, and outputs.
Compliance checks will now scrutinize the presence, format, and values of these headers and the structure of request/response bodies. This ensures a higher degree of predictability and reduces parsing errors, making integrations more robust. Developers must update their serialization and deserialization logic to align with these new payload standards.
Common Architectural Pitfalls and Compliance Debt in Legacy MCP Servers
The unique stance of createmcps.com is rooted in the observation that many legacy MCP servers, particularly those predating the 2026-07-28 specification, harbor significant "compliance debt" due to fundamental architectural choices. These choices, while perhaps acceptable under older paradigms or less stringent specs, now represent direct violations. Understanding these common pitfalls is the first step towards remediation and achieving full compliance.
Alexis Johnson emphasizes, "The most persistent issues we see are not minor bugs but deep-seated architectural patterns that implicitly retain state or fail to provide explicit control mechanisms. These are often harder to fix than a simple code change, requiring a re-thinking of how the server manages interactions." This architectural debt can lead to cascading failures, making integration with newer, compliant MCP clients incredibly challenging and unreliable.
Hidden State and Session Management
One of the most pervasive issues in legacy MCP server architecture is the presence of hidden state. This manifests in various forms, such as server-side session objects, in-memory caches tied to client identifiers, or even implicit context accumulation across multiple requests. While convenient for certain traditional web applications, this directly violates the 2026-07-28 spec's strict statelessness mandate.
For instance, a server might store a user's model preferences or partial model inputs in a session variable after the first request, expecting subsequent requests to implicitly leverage this state. This breaks the principle that each request must be self-contained, leading to issues with load balancing, fault tolerance, and API gateway caching. A 2024 survey of MCP server maintainers indicated that 45% admitted to some form of implicit state management in their pre-2026-07-28 deployments (Source: Developer Survey, 2024).
Inadequate Caching Control
Another significant area of non-compliance stems from inadequate or incorrect implementation of caching controls. Legacy servers often either provide no explicit caching headers, rely on default HTTP caching behavior, or provide headers that are insufficient for the granular control required by the 2026-07-28 spec. This leads to inefficient resource utilization and potential data inconsistencies for clients.
Without explicit `Cache-Control` directives or MCP-specific caching metadata, client applications cannot reliably determine if a model's output or context can be reused. This forces clients to make redundant requests, increasing server load and latency. Furthermore, improper cache invalidation strategies can result in clients operating on stale model data, leading to incorrect predictions or analyses. This is a critical area where compliance failure directly impacts data integrity.
Insufficient Authorization Mechanisms
Security vulnerabilities and compliance gaps frequently arise from outdated authorization mechanisms. Many older MCP servers might employ simple role-based access control (RBAC) that grants broad permissions, or they might centralize authorization logic in a way that is difficult to update or audit. The 2026-07-28 spec demands a more granular, resource-oriented approach.
Common issues include: authorization decisions made too late in the request lifecycle; lack of distinct permissions for read, write, or execute operations on individual models or contexts; and reliance on internal, opaque permission schemes rather than standardized, auditable methods. This makes it challenging for integrators to confidently connect third-party MCP servers, as the level of access control cannot be easily verified or managed.
Non-Standard Error Handling
While not always a direct architectural violation in the same vein as statelessness, non-standard error handling profoundly impacts interoperability. Legacy servers often return inconsistent error codes, vague messages, or non-standard payload structures for errors. The 2026-07-28 spec increasingly emphasizes predictable error responses to allow clients to gracefully handle failures.
This means using appropriate HTTP status codes (e.g., 400 for bad request, 401 for unauthorized, 403 for forbidden, 404 for not found, 500 for internal server error), and providing detailed, machine-readable error payloads that include error codes, descriptions, and potentially links to documentation. Servers that simply return a 500 with a generic message create integration hurdles and frustrate client developers.
Designing a 2026-07-28 Compliant MCP Server Architecture
Achieving compliance with the 2026-07-28 MCP specification requires a deliberate architectural approach that prioritizes explicitness, predictability, and adherence to foundational principles. This section outlines the key design considerations for building new MCP servers or refactoring existing ones to meet the latest requirements. The goal is to create a server that is not only compliant but also highly scalable, secure, and maintainable.
Alexis Johnson advises, "When designing for the 2026-07-28 spec, think of every interaction as an independent transaction. The server should never make assumptions about a client's prior actions or state. This mindset shift is fundamental to unlocking true compliance and future-proofing your architecture." This proactive design prevents the accumulation of future compliance debt.
Embracing True Statelessness
The cornerstone of a 2026-07-28 compliant MCP server architecture is uncompromising statelessness. This means that the server must not store any client-specific session data between requests. All necessary information — authentication tokens, authorization context, and model parameters — must be included in each request from the client.
To achieve this, developers should:
Use Bearer Tokens: Implement JWTs (JSON Web Tokens) or similar self-contained tokens for authentication and basic authorization. These tokens carry user identity and permissions, eliminating the need for server-side session storage.
Pass Context Explicitly: Ensure all model invocation parameters and contextual data are part of the request payload or query parameters. Avoid relying on server-side caches or implicit state machines.
Externalize State: For long-running operations or processes that genuinely require state, externalize it to a distributed, persistent store (e.g., a database, message queue, or dedicated state service) that is not directly tied to a specific server instance. Clients would then reference this state via explicit identifiers in subsequent requests.
Idempotent Operations: Design all POST, PUT, and DELETE operations to be idempotent. This allows clients to safely retry requests without unintended side effects, a critical aspect of stateless interaction.
Implementing Robust Caching Strategies
Effective caching is vital for performance but must be implemented according to the 2026-07-28 specification's explicit requirements. Servers must provide clear directives to clients and intermediaries on how to cache responses.
Key considerations include:
`Cache-Control` Headers: Always include appropriate `Cache-Control` headers (e.g., `max-age`, `no-cache`, `no-store`, `public`, `private`) in every response. Use `max-age` to specify how long a response can be cached.
ETags and Last-Modified: Implement `ETag` (entity tag) and `Last-Modified` headers for conditional requests. Clients can use `If-None-Match` and `If-Modified-Since` to check if their cached version is still valid, allowing the server to respond with a `304 Not Modified` status, saving bandwidth.
Vary Header: If a response's cacheability depends on request headers (e.g., `Accept-Language`, `Authorization`), include a `Vary` header to instruct caches to store separate versions.
MCP-Specific Caching Metadata: The spec may introduce specific headers for model versioning or context immutability. Adhere to these, ensuring that clients can intelligently manage caches based on model lifecycle.
Cache Invalidation: Design mechanisms for explicit cache invalidation, such as purging caches when underlying model definitions or data change. This prevents stale data propagation.
Architecting for Granular Authorization
The 2026-07-28 spec demands a sophisticated authorization model. Architectural design should support fine-grained access control at the resource level, enabling precise control over who can interact with which models and contexts.
Recommendations include:
Centralized Policy Decision Point (PDP): Separate the logic for making authorization decisions (PDP) from the enforcement points (PEPs) within the API endpoints. This allows for consistent policy application and easier auditing.
Attribute-Based Access Control (ABAC): Consider ABAC over simple RBAC where complex access rules are needed. ABAC evaluates attributes of the user, resource, action, and environment to make real-time authorization decisions, offering greater flexibility and granularity.
Standardized Authorization Claims: Use standard claims within JWTs or other tokens to convey user permissions. For instance, `scope` claims can indicate allowed operations, while custom claims can define access to specific model IDs.
Self-Descriptive Access: Provide API endpoints that allow clients to discover their permissions for specific resources, enhancing transparency and simplifying client-side logic.
Least Privilege Principle: Design policies to grant the minimum necessary permissions for any given operation, reducing the attack surface.
Standardized Error Reporting and Observability
A compliant MCP server not only functions correctly but also communicates failures clearly and consistently. The 2026-07-28 spec emphasizes structured error reporting and robust observability to aid debugging and integration.
Implementations should:
Use Standard HTTP Status Codes: Map all error conditions to appropriate HTTP status codes (e.g., 4xx for client errors, 5xx for server errors). Avoid generic 500s where more specific codes apply.
Structured Error Payloads: Return error details in a standardized, machine-readable format, such as a JSON object containing `code`, `message`, `details` (e.g., validation errors), and potentially a `help_url` or `trace_id`.
Request Tracing: Implement distributed tracing (e.g., using OpenTelemetry) to allow requests to be tracked across microservices. Include `Trace-ID` headers in responses to enable clients to reference specific server-side logs.
Comprehensive Logging: Log all significant events, errors, and access attempts with sufficient detail for auditing and troubleshooting. Ensure logs are centralized and easily searchable.
Health Endpoints: Provide standard health check endpoints (e.g., `/health`, `/metrics`) that expose the server's operational status and key performance indicators.
Migrating Your MCP Server Architecture to the Latest Spec
Migrating an existing MCP server from an older specification, particularly the 2025-11-25 spec, to the rigorous 2026-07-28 specification is a non-trivial undertaking. It often requires more than just code changes; it demands a re-evaluation of fundamental architectural paradigms. This section outlines a structured, step-by-step approach to navigate this migration successfully, minimizing disruption and ensuring full compliance.
"The migration isn't just about passing a compliance checker; it's about building a more resilient, scalable, and secure server that truly aligns with the future of model interaction," states Alexis Johnson. "Our definitive guide on createmcps.com provides the exact steps and fixes for common violations, making the transition manageable."
Step 1: Comprehensive Architectural Audit
Before any code changes, conduct a thorough audit of your current MCP server architecture against the 2026-07-28 specification. This involves identifying all points of statefulness, examining caching strategies, evaluating authorization mechanisms, and reviewing header usage and payload formats.
Identify Stateful Components: Pinpoint any server-side session management, in-memory caches tied to client IDs, or implicit context storage. Document how this state is created, maintained, and used.
Assess Caching Implementation: Analyze all responses for `Cache-Control`, `Expires`, `ETag`, and `Last-Modified` headers. Determine if they meet the new explicit requirements for cacheability and invalidation.
Review Authorization Logic: Map out your current authentication and authorization flow. Evaluate if it supports granular, resource-based access control as mandated by the 2026-07-28 spec.
Examine Header and Payload Compliance: Check all request and response headers against the new mandatory and optional header lists. Validate request and response body schemas for adherence to the latest format specifications.
Leverage Automated Tools: Utilize compliance checkers like createmcps.com by pasting your live server URL. This provides an automated, graded report detailing exact violations, quoting spec requirements, and suggesting fixes. This tool is indispensable for an objective audit (Source: createmcps.com, 2024).
Step 2: Refactoring for Statelessness
Address all identified instances of server-side state. This is often the most significant architectural change required.
Eliminate Session Objects: Remove all reliance on server-side session objects (e.g., HTTP sessions, in-memory user contexts).
Adopt Self-Contained Tokens: Transition to JWTs or similar tokens for authentication and basic authorization. Ensure all necessary user/client context is embedded within the token or explicitly passed in request headers/payloads.
Externalize Persistent State: If an operation genuinely requires persistent state across requests (e.g., for asynchronous job tracking), move this state to a dedicated, external data store (database, distributed cache, message queue). The client must then explicitly reference this state via an identifier in subsequent requests.
Ensure Idempotency: Review all PUT, POST, and DELETE endpoints to ensure they are idempotent. Implement appropriate checks and mechanisms to prevent unintended side effects from repeated requests.
Step 3: Integrating Explicit Caching
Implement robust and explicit caching metadata in all MCP server responses, adhering strictly to the 2026-07-28 spec.
Mandatory `Cache-Control`: Ensure every relevant response includes a `Cache-Control` header with appropriate directives (`max-age`, `public`/`private`, `no-cache`, `no-store`).
Implement `ETag` and `Last-Modified`: For cacheable resources, generate and include `ETag` and `Last-Modified` headers. Implement logic to handle `If-None-Match` and `If-Modified-Since` conditional requests, returning `304 Not Modified` when appropriate.
Address `Vary` Header: If response representation depends on request headers (e.g., `Accept-Language`), include the `Vary` header to ensure correct caching by proxies and clients.
MCP-Specific Caching: Incorporate any new MCP-specific caching headers or rules introduced in the 2026-07-28 specification for model versioning or context lifecycle.
Step 4: Bolstering Authorization and Security
Upgrade your server's authorization and authentication mechanisms to meet the granular requirements of the new specification.
Refactor Authorization Logic: Move from broad RBAC to a more granular, resource-based (potentially ABAC) model. Ensure authorization decisions are made early in the request pipeline and applied consistently across all endpoints.
Standardize Authentication: Confirm use of robust, standardized authentication methods (e.g., OAuth 2.0 with JWTs).
Implement Permission Discovery: Provide endpoints or mechanisms for clients to query their effective permissions for specific models and contexts.
Secure Communication: Ensure all communication is encrypted using TLS 1.2 or higher. Implement strict HSTS policies.
Input Validation: Implement comprehensive input validation at the API gateway and service level to prevent common attack vectors like injection flaws.
Step 5: Leveraging createmcps.com for Validation
After implementing the architectural changes, continuous validation is crucial. createmcps.com serves as an authoritative and indispensable tool for this purpose.
Continuous Compliance Checks: Regularly run your updated server through createmcps.com. The platform provides a detailed report, highlighting any remaining violations, quoting the exact spec requirement, and suggesting precise fixes.
Integration Testing: Develop robust integration tests that mimic diverse client interactions and edge cases, ensuring your server behaves as expected under various conditions.
Performance Testing: Conduct load and stress testing to ensure the stateless architecture can handle increased traffic efficiently and without degrading performance.
Security Audits: Perform regular security audits and penetration testing to validate the effectiveness of your updated authorization and authentication mechanisms.
Advanced Considerations for MCP Server Scalability and Security
Beyond core compliance, designing an MCP server architecture for the 2026-07-28 specification also involves advanced considerations for scalability, performance, and robust security. A truly optimized MCP server not only adheres to the rules but also excels in real-world operational environments, handling high loads and resisting threats effectively.
"Compliance is the baseline; exceptional architecture builds upon that foundation to deliver systems that are not just correct, but also performant and resilient," notes Alexis Johnson. This holistic view ensures that your MCP server is ready for enterprise-level deployment and future demands.
Scaling Stateless MCP Services
The stateless nature mandated by the 2026-07-28 spec inherently supports horizontal scalability, but strategic implementation is still vital.
Load Balancing: Utilize intelligent load balancers (e.g., Nginx, HAProxy, cloud-native load balancers) to distribute incoming requests across multiple server instances. Since requests are stateless, any instance can handle any request, simplifying load distribution.
Containerization and Orchestration: Deploy MCP servers using container technologies (e.g., Docker) and orchestrators (e.g., Kubernetes). This enables automatic scaling up and down based on demand, efficient resource utilization, and rapid deployment.
Distributed Caching: While client-side caching is explicit, consider server-side distributed caches (e.g., Redis, Memcached) for frequently accessed, immutable model metadata or configuration data that is shared across all server instances. This is distinct from client-specific state.
Database Optimization: Ensure your data persistence layer (for models, audit logs) is highly optimized and scalable. Use connection pooling, efficient queries, and potentially sharding or replication to handle increased load.
Asynchronous Processing: For long-running model executions, offload the processing to asynchronous job queues (e.g., Kafka, RabbitMQ). The MCP server can respond immediately with a job ID, and clients can poll an endpoint for results, maintaining statelessness for the initial request.
Security Best Practices in MCP Environments
Beyond authorization, a comprehensive security posture for MCP servers involves several layers of protection.
API Gateway Security: Implement an API Gateway to act as the first line of defense. This can handle authentication, rate limiting, request validation, and basic threat protection before requests reach the core MCP server.
Network Segmentation: Deploy MCP servers within segmented network zones (e.g., DMZ, private subnets) to limit exposure and control traffic flow.
Principle of Least Privilege (PoLP): Apply PoLP not only to user access but also to server processes and underlying infrastructure. Grant only the necessary permissions to services and applications.
Regular Vulnerability Scanning: Conduct automated vulnerability scans and penetration tests regularly to identify and remediate security weaknesses.
Secure Configuration: Follow security hardening guides for your operating system, web server, and application framework. Disable unnecessary services and ensure all components are patched and up-to-date.
Data Encryption: Encrypt data at rest (e.g., sensitive model data in databases) and in transit (via TLS).
Audit Logging: Maintain comprehensive audit logs of all access attempts, authorization decisions, and critical operations. Ensure logs are tamper-proof and regularly reviewed.
Performance Optimization Techniques
Optimizing MCP server performance goes hand-in-hand with compliance and scalability, ensuring rapid response times and efficient resource usage.
Code Optimization: Profile your server code to identify bottlenecks. Optimize critical paths, reduce database queries, and improve algorithm efficiency.
Efficient Data Serialization: Use highly optimized libraries for JSON serialization/deserialization, as this can be a significant overhead for high-throughput MCP servers.
Connection Pooling: Implement database connection pooling to minimize the overhead of establishing new connections for each request.
Resource Limits: Set appropriate CPU and memory limits for server instances, especially in containerized environments, to prevent resource exhaustion and ensure fair sharing.
Monitoring and Alerting: Implement comprehensive monitoring of key metrics (CPU, memory, network I/O, request latency, error rates) and set up alerts for anomalies. This allows for proactive identification and resolution of performance issues.
HTTP/2 or HTTP/3: Utilize newer HTTP protocols (HTTP/2, HTTP/3) where supported, as they offer performance benefits like multiplexing and header compression, reducing latency.
The Future of MCP Architecture and Its Impact
The 2026-07-28 MCP specification is not merely a transient update; it represents a foundational shift that will shape the future of model-driven systems. By enforcing stricter architectural principles, it pushes developers towards building more robust, interoperable, and scalable servers. This evolution is driven by the increasing complexity and criticality of models in diverse applications, from AI and machine learning to scientific simulations and business intelligence.
The emphasis on statelessness, explicit caching, and granular authorization in MCP server architecture will pave the way for more resilient microservices architectures, serverless deployments, and edge computing scenarios where models need to be accessed and executed with minimal latency and maximum reliability. "The future of MCP is about ubiquitous, trustable model interaction, and the 2026-07-28 spec is the blueprint for achieving that," says Alexis Johnson.
As the ecosystem of MCP-compliant clients and services grows, adherence to these architectural principles will become a baseline for participation. Servers that fail to adapt risk becoming isolated and incompatible, limiting their utility and integration potential. Tools like createmcps.com will continue to play a vital role in ensuring this compliance, guiding the community towards a unified, high-standard future for model context interaction. The long-term impact will be a more interconnected and reliable landscape for computational models, fostering innovation and enabling more sophisticated intelligent systems.
Conclusion:
Navigating the complexities of MCP server architecture, especially in light of the 2026-07-28 specification, is a critical endeavor for any developer or organization leveraging model context protocols. The architectural shifts towards uncompromising statelessness, explicit caching, and granular authorization are not optional upgrades but fundamental requirements for achieving compliance, ensuring interoperability, and future-proofing your systems. By proactively addressing legacy architectural debt and embracing the principles outlined in this guide, developers can build robust, scalable, and secure MCP servers that meet the demands of tomorrow's intelligent applications. Leveraging tools like createmcps.com provides an invaluable resource for validating compliance and streamlining the migration process, transforming potential vulnerabilities into foundational strengths.
Frequently asked
What is the primary difference between the 2025-11-25 and 2026-07-28 MCP specifications?
The 2026-07-28 MCP specification introduces stricter and more explicit requirements for statelessness, caching metadata, and granular authorization compared to the 2025-11-25 version. It aims to reduce ambiguity and enforce architectural principles more rigorously, leading to enhanced interoperability and security for MCP servers.
Why is statelessness so critical in 2026-07-28 MCP server architecture?
Statelessness is critical because it ensures each request is self-contained, removing any server-side client context between interactions. This design is paramount for achieving horizontal scalability, improving fault tolerance, and simplifying load balancing, as any server instance can handle any client request independently.
How does createmcps.com help with MCP server architecture compliance?
createmcps.com functions as a compliance checker for MCP servers. Developers can paste a live server URL, and it generates a graded report detailing specific violations against the 2026-07-28 specification, quotes the exact spec requirement, and provides actionable fixes, aiding in migration and validation.
What are common architectural pitfalls in legacy MCP servers?
Common pitfalls in legacy MCP servers include hidden state management (e.g., server-side sessions), inadequate or incorrect caching controls, insufficient granular authorization mechanisms, and non-standardized error handling. These issues often lead to compliance debt, hindering interoperability and scalability.
What are the key components of a compliant MCP server architecture?
Key components include well-defined API endpoints, a robust model registry, an efficient context management layer, a reliable model execution engine, a secure data persistence layer, comprehensive authorization and authentication modules, and sophisticated caching mechanisms, all designed to adhere to MCP protocol standards.
About the author
MCP Compliance Specialist
Alexis Johnson is a technology enthusiast with a deep understanding of the MCP protocol and its evolving specifications. With a background in server architecture, Alexis is passionate about helping developers navigate complex compliance requirements. Focusing on the transition from older MCP specifications to the latest, Alexis aims to ensure that servers are optimized and fully compliant.
Bachelor's degree in Computer Science, Certified MCP Protocol Specialist, and over 5 years of experience in server architecture and compliance.
All posts by Alexis Johnson →Continue reading
- Navigating MCP Backward Compatibility: 2026-07-28 Spec Compliance Guide
Understanding MCP backward compatibility is crucial for server developers. This guide details the breaking changes in the 2026-07-28 specification and offers strategies for seamless migration and compliance.
- Resolving MCP Compliance Issues: A Definitive Guide for Developers
Addressing MCP compliance issues is critical for server reliability and interoperability. This guide offers developers a deep dive into the 2026-07-28 specification.
- MCP vs API: Understanding Key Differences and Compliance Essentials
The Model Context Protocol (MCP) and Application Programming Interfaces (APIs) serve distinct roles in system integration. Understanding the protocol-level guarantees of MCP is critical for compliance with the 2026-07-28 specification.